
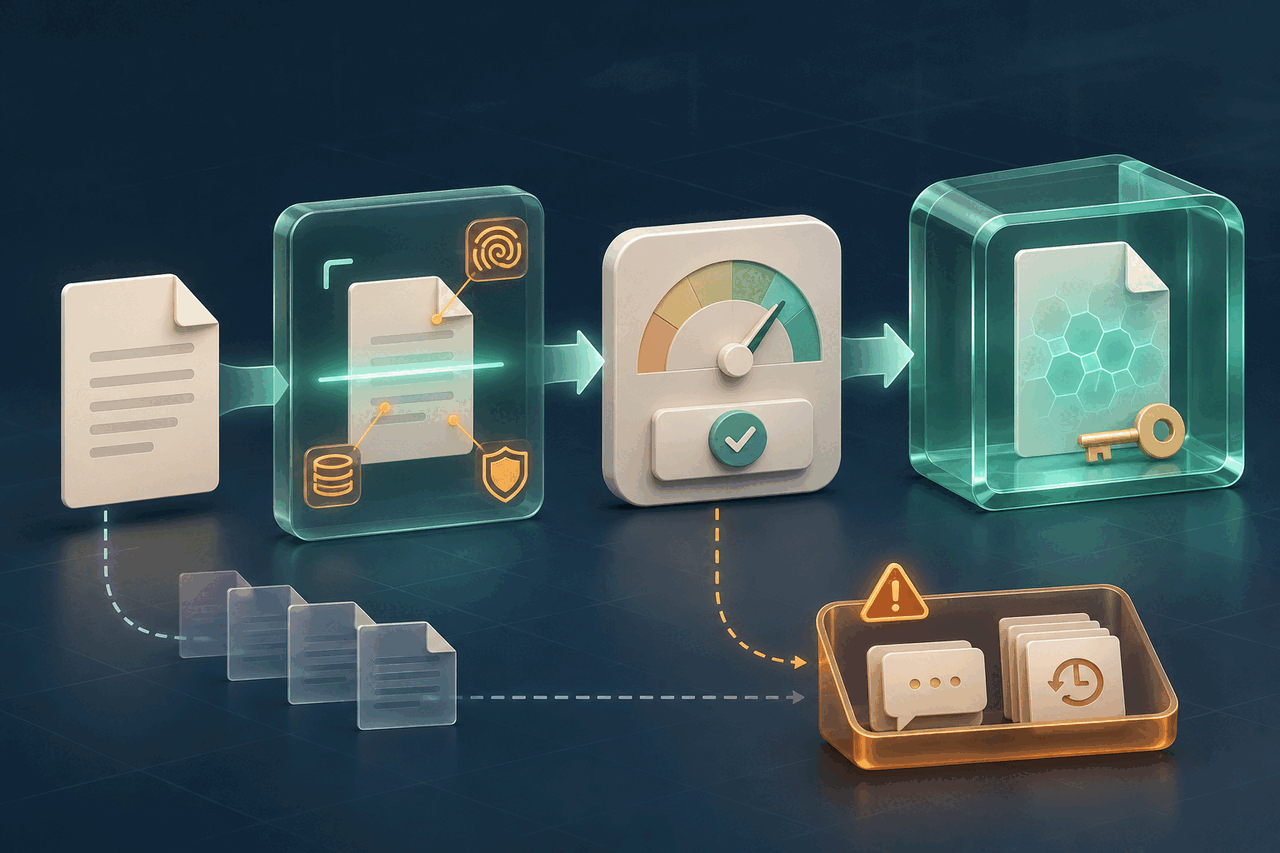
Automatic protection sounds safer than asking every person to recognise sensitive content and remember an extra step. Google Workspace's latest beta can apply client-side encryption when a Drive file matches an administrator's data-protection rule. The same automation can also change how a file works, so the safest first move is observation—not immediate enforcement.
What Google announced on 5 November
Google introduced Policy-Based Enforcement for client-side encryption in beta on 5 November 2026. Administrators can define Workspace Rules that find matching files in My Drive and shared drives, then encrypt them in place while preserving the original URL. Google lists Docs, Sheets, Slides, Microsoft Office files, PDFs and images among the supported content.
This is a limited enterprise beta, not a switch available to every Drive account. It is off by default, requires enrolment, an eligible Assured Controls setup, client-side encryption configuration, an identity provider and an external Key Access Control List Service (KACLS). Users cannot configure the rule themselves; they see a notice after an administrator's policy applies encryption.
Why a pilot matters
Google's administrator guidance, updated 5 November, documents consequential side effects. When a native Workspace file is converted, linked Forms and container-bound Apps Script automations stop and are removed from the primary file. Previous unencrypted revisions are deleted, and third-party comments in Microsoft Office files are removed. The removed material is exported to encrypted takeout files, but that is not the same as retaining every feature in the working document.
A key-service failure has another important outcome: the file remains unencrypted and Workspace raises an alert. A rule therefore needs monitoring and a verified response process, not an assumption that every match became protected.
An audit-first rollout checklist
1. Map dependencies before content. Inventory linked Forms, scripts, comments, revision-history needs, external collaborators, preview requirements and approved recovery routes. Include PDFs that depend on signatures, forms or specialist viewers. 2. Start with an audit-only rule. Google's guidance recommends measuring matched files before choosing the encryption action. Review false positives and files that should never be converted automatically. 3. Test synthetic or authorised samples. Use each important file type and workflow. Confirm who can decrypt, preview, download and restore the sample, and record what happens to comments, integrations and revisions. 4. Exercise failure handling. Simulate the approved response to a KACLS alert. Confirm that administrators can identify files left unencrypted, fix the service issue, rescan and verify a successful encryption event. 5. Expand in small stages. Apply the rule to a controlled organisational unit or group, monitor rule logs and obtain sign-off from security, records, legal and business owners before widening scope.
Encryption is not a complete document check
Policy-based CSE controls who can decrypt content; it does not prove the PDF is accurate, accessible, malware-free or ready to send. It also does not replace retention, sharing or incident-response policy.
Keep confidential Workspace files inside the approved environment. For a separate, authorised and decrypted working copy, FileStation's PDF Reader can support a visual page check, and the CLEAR document check offers a simple release routine. FileStation does not connect to Google Workspace CSE, manage encryption keys or carry Drive controls into a downloaded PDF.
The useful promise of this beta is consistent enforcement. The responsible route to that consistency is a measured pilot that proves the rule protects the right files without quietly breaking the work around them.